
The lifeblood of any devops team is speed. Code goes from commit to prod in minutes instead of weeks and any security control that cannot go at that speed ends up getting ignored or simply skipped over. Cloud security, when executed well, does not need to be the Achilles heel of velocity and that is good news! In fact, many of the mechanisms that keep cloud environments secure were designed to take these kinds of fast-paced, automated workflows into account and understanding those advantages shifts how DevOps teams even think about security from a hindrance into an inbuilt benefit.
Connecting those dots for you in terms of the cloud security benefits for DevOps workflows, because this way, security is literally depicted as something that can act with as much speed of deployment (early game implementation in your ongoing build and development processes) instead of lagging behind like an embarrassing 90s sitcom.
Automation Fits the DevOps Mindset
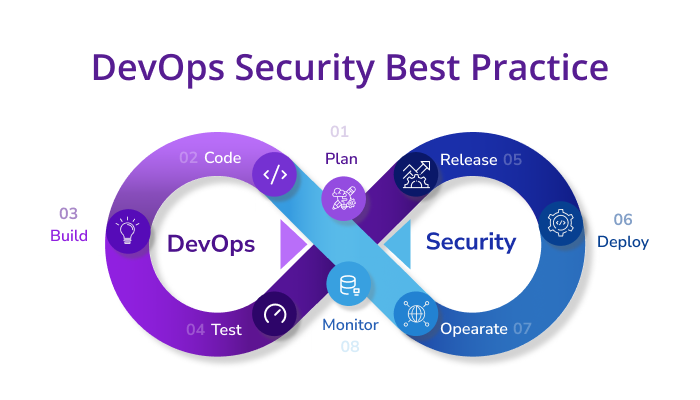
Automation is the single most significant benefit of cloud security for DevOps. Instead of manually reviewing configuration checks, vulnerability scans, and identity policy enforcement before every release, these measures can run as a background process at all times. If your team already treats infrastructure as code and pipelines as the core of delivery, incorporating security scans into that automated flow is a natural progression rather than an awkward attachment.
It’s also a significant change from the old model of how security used to function. Checks run in the same CI/CD pipeline that handles testing and deployment instead of a separate team reviewing a build right before it goes out, catching problems when a dev is still in the context of that change. Particular guidance on wiring these checks directly into pipeline automation, the best practices surrounding CI/CD pipeline security from secret management to least-privilege permissions for automated jobs building & deploying code.
Accelerated Feedback Loops Identify Challenges Sooner
This means that errors in constructing and testing software do not reach production, halting security issues, but cloud-native scanning tools provide feedback on these issues almost as quickly as developers get feedback on failing tests. You can flag a dependency with a known vulnerability, hardcoded credential, or overly permissive access policy in seconds when it lands in a pull request rather than months later during an audit. This means that the person who created the problem is also the best person to resolve it quickly because the context is still fresh.
And that speed is a bigger deal than it seems. Fixing a vulnerability encountered in pull request might take you just a few minutes to fix. But the same vulnerability detected post-deployment could trigger an incident response process, a rollback, and a much larger time commitment. Implementing dedicated cloud security tooling for the DevOps environments bridges that gap by bringing detection as near the point of creation as possible.
Automation-ready Identity and Secrets management
DevOps pipelines operate continuously, running automated actions that require authorization to cloud resources, and long-lived credentials don’t work for this pattern. Modern cloud identity solutions allow for short-lived, automatically rotating credentials that a pipeline can request at runtime, which expire shortly after, significantly reducing the time an attacker would benefit if ever compromised.
When centralized secrets management is paired with that, it means never needing to have API keys or database passwords or any other kind of sensitive value in a repository nor anywhere else within a configuration file. This single change eliminates one of the most common ways credentials are inadvertently exposed for DevOps teams running dozens or hundreds of automated jobs.
Consistency Across Every Environment
One particularly overlooked advantage of cloud security for DevOps is its consistency. This also means that the same security policies protecting production can be used precisely as is in staging, testing, and development environments, thereby eliminating any drift that previously allowed vulnerabilities to evade detection lower in the application stack, only to rear their heads again in production later. A security control should be defined once and applied across all environments via the same pipeline so that no environment sees it die a silent death.
This consistency also shows up in how quickly the industry is investing in tools built specifically for this intersection of development and security. A startup automating security as code illustrates the scale of that investment, describing a funding round aimed squarely at giving engineering teams pre-built, codified security workflows rather than requiring each team to assemble its own from scratch.
Why This Shifts Up the DevOps Dialogue
The older paradigm of security as a gate that slows delivery no longer holds up to the reality of what cloud-native tooling can do today. Using automated scanning and short-lived credentials, the implementation of security policy across every environment means that security can run at a velocity matching the rest of the pipeline instead of behind it. The shift for DevOps teams is less about doing more work and more about enabling them to do the same work with far less manual overhead, especially under constant pressure to ship faster.
Frequently Asked Questions
Does cloud security scanning add latency to CI/CD pipelines?
Scanning is fast and it runs in parallel with existing build and test steps, adding very little time. The trade off is almost always in favor compared to weighing the cost of catching that same issue after deployment.
Who owns security in a DevOps pipeline, the developers or a dedicated security team?
In a more mature DevOps environment, this is treated as a shared responsibility where the developers own the automated checks that are built into their pipeline while a smaller security team focuses on policy, tooling and the highest-impact findings.
What is the most prominent security risk associated with DevOps automation?
Amongst the most prevalent threats are long-lived credentials hardcoded into pipeline configurations, because once a key is exposed, it can provide extensive access until it is manually rotated or revoked.
